
LATEST FORTINET NSE6_OTS_AR-7.6 EXAM COST - NSE6_OTS_AR-7.6 TEST
P.S. Free & New NSE6_OTS_AR-7.6 dumps are available on Google Drive shared by FreePdfDump: https://drive.google.com/open?id=1afm8ZcfXAoSYY6kuUc4R0bkR_VRri4AK
Although at this moment, the pass rate of our NSE6_OTS_AR-7.6 exam braindumps can be said to be the best compared with that of other exam tests, our experts all are never satisfied with the current results because they know the truth that only through steady progress can our NSE6_OTS_AR-7.6 Preparation materials win a place in the field of exam question making forever. Therefore, buying our NSE6_OTS_AR-7.6 actual study guide will surprise you with high grades.
Fortinet NSE6_OTS_AR-7.6 Exam Overview:
| Certification Vendor: | Fortinet |
|---|---|
| Exam Name: | Fortinet NSE 6 - OT Security 7.6 Architect |
| Exam Number: | NSE6_OTS_AR-7.6 |
| Passing Score: | 60-70% |
| Certificate Validity Period: | 2 years |
| Related Certifications: | Fortinet NSE 4 Fortinet NSE 5 Fortinet NSE 6 Fortinet NSE 7 |
| Exam Duration: | 60 minutes |
| Real Exam Qty: | 30-40 |
| Exam Price: | USD 200 |
| Exam Format: | Multiple response, Multiple choice, Proctored exam |
| Available Languages: | English |
| Recommended Training: | Fortinet Training Institute - OT Security Courses Fortinet NSE 6 OT Security Training Path |
| Exam Registration: | Fortinet Certification Portal Pearson VUE Registration |
| Sample Questions: | Fortinet NSE6_OTS_AR-7.6 Sample Questions |
| Exam Way: | Online proctored or testing center (Pearson VUE) |
| Pre Condition: | Recommended: Fortinet NSE 4 certification or equivalent networking and security knowledge |
| Official Syllabus URL: | https://www.fortinet.com/training-certification |
>> Latest Fortinet NSE6_OTS_AR-7.6 Exam Cost <<
NSE6_OTS_AR-7.6 Test Questions Answers & Real NSE6_OTS_AR-7.6 Exam Questions
Our company is a multinational company which is famous for the NSE6_OTS_AR-7.6 training materials in the international market. After nearly ten years' efforts, now our company have become the topnotch one in the field, therefore, if you want to pass the NSE6_OTS_AR-7.6 exam as well as getting the related certification at a great ease, I strongly believe that the NSE6_OTS_AR-7.6 Study Materials compiled by our company is your solid choice. To be the best global supplier of electronic NSE6_OTS_AR-7.6 study materials for our customers' satisfaction has always been our common pursuit.
Fortinet NSE6_OTS_AR-7.6 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Fortinet NSE 6 - OT Security 7.6 Architect Sample Questions (Q97-Q102):
NEW QUESTION # 97
According to the IEC 62443 standard, your security level is 4. What is your OT environment defending against? (Choose one answer)
- A. Intentional cyberthreats posed by skilled malicious users
- B. An intentional attack with low resources
- C. A casual exposure
- D. A syndicate of cyber extortion with extensive resources
Answer: D
Explanation:
According to the OT Security 7.6 Architect study guide regarding IEC 62443 Security Levels:
Security Level 4 (SL 4) Definition: This level provides "Protection against intentional violation using sophisticated means with extended resources, specific skills, and high motivation".
Real-World Application: The study guide specifically notes: "If you are facing a syndicate of cyber extortionists with extensive resources and capabilities, then you should strive for security level 4".
Comparison to other levels:
SL 1: Protection against "casual or unintentional system violation".
SL 2: Protection against "intentional violation using simple means with low resources".
SL 3: Protection against "intentional violation using sophisticated means with moderate resources".
NEW QUESTION # 98
Refer to the exhibit.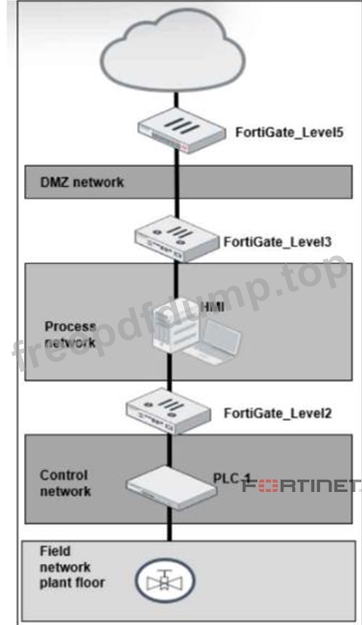
A simplified OT network is shown. You want to optimize the protection of this OT network. Which two controls must you implement? (Choose two answers)
- A. Offline IDS on FortiGate_Level3.
- B. Virtual patching on FortiGate_Level2.
- C. IPS on FortiGate_Level5.
- D. OT signature on FortiGate_Level5.
Answer: B,C
Explanation:
The correct answers are B. IPS on FortiGate_Level5 and C. Virtual patching on FortiGate_Level2.
The study guide explains that "the first line of defense is securing the IT side of your network" and that FortiGate should be placed to protect ICS environments and stop threats from propagating from IT into OT. It also states that IPS improves OT security because "today's threat landscape requires IPS to block a wider range of threats and improve OT security" and that in IPS mode, vulnerable devices are protected. This makes FortiGate_Level5, at the upper boundary near the DMZ and external connectivity, the correct place to implement IPS as a primary protection control.
The study guide also states in the Purdue model section that "Level 2 consists of the processes and programs that control the PLCs, RTUs, and IEDs found at Level 1" and that "it is necessary to segment, or even microsegment, these servers with firewall segmentation, along with policies that include application control and virtual patching." In addition, the virtual patching section says "Virtual patching protects OT devices that have not yet been updated against vulnerability exploits" and applies when traffic related to the vulnerable device reaches the firewall policy. Since FortiGate_Level2 sits between the process network and the control network, it is the right enforcement point for virtual patching to protect the PLC-side assets.
Option A is not one of the best answers because offline IDS only detects and logs attacks; the guide says "no traffic flows through FortiGate" in offline IDS mode, whereas IPS can actually block threats. Option D is also not the best answer because OT signatures are enabled within the IPS framework, but the stronger control explicitly described for this design is to deploy IPS at the upper boundary and virtual patching closer to vulnerable OT devices.
NEW QUESTION # 99
Refer to the exhibit.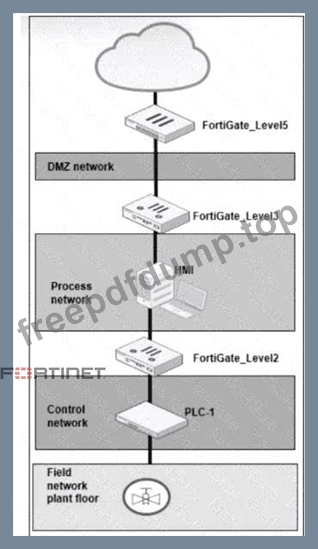
A simplified OT network is shown. You want to optimize the protection of this OT network. Which two controls must you implement? (Choose two answers)
- A. Offline IDS on FortiGate_Level3.
- B. Virtual patching on FortiGate_Level2.
- C. IPS on FortiGate_Level5.
- D. OT signature on FortiGate_Level5.
Answer: B,C
Explanation:
The correct answers are B. IPS on FortiGate_Level5 and C. Virtual patching on FortiGate_Level2 .
The study guide explains that "the first line of defense is securing the IT side of your network" and that FortiGate should be placed to protect ICS environments and stop threats from propagating from IT into OT. It also states that IPS improves OT security because "today's threat landscape requires IPS to block a wider range of threats and improve OT security" and that in IPS mode, vulnerable devices are protected . This makes FortiGate_Level5 , at the upper boundary near the DMZ and external connectivity, the correct place to implement IPS as a primary protection control.
The study guide also states in the Purdue model section that "Level 2 consists of the processes and programs that control the PLCs, RTUs, and IEDs found at Level 1" and that "it is necessary to segment, or even microsegment, these servers with firewall segmentation, along with policies that include application control and virtual patching." In addition, the virtual patching section says "Virtual patching protects OT devices that have not yet been updated against vulnerability exploits" and applies when traffic related to the vulnerable device reaches the firewall policy. Since FortiGate_Level2 sits between the process network and the control network, it is the right enforcement point for virtual patching to protect the PLC-side assets.
Option A is not one of the best answers because offline IDS only detects and logs attacks; the guide says "no traffic flows through FortiGate" in offline IDS mode, whereas IPS can actually block threats. Option D is also not the best answer because OT signatures are enabled within the IPS framework, but the stronger control explicitly described for this design is to deploy IPS at the upper boundary and virtual patching closer to vulnerable OT devices .
NEW QUESTION # 100
Refer to the exhibit.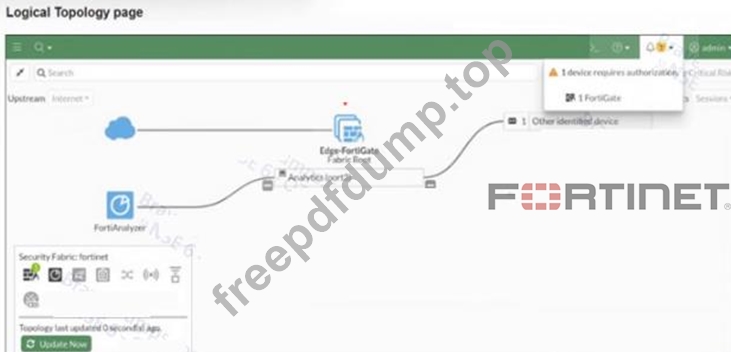
A Logical Topology page of a FortiGate device is shown. Your OT company wants to gain visibility into the network. You decide to implement device detection with the Security Fabric. Based on the exhibit, which statement is correct? (Choose one answer)
- A. Device Detection is enabled on port3.
- B. The other identified device must be authorized on the root FortiGate.
- C. The other identified device must be authorized on FortiAnalyzer.
- D. Device Detection is enabled on the other identified device.
Answer: D
Explanation:
The correct answer is A. Device Detection is enabled on the other identified device.
The study guide explains that device identification is a "useful feature for the Security Fabric topology view" and that "FortiGate detects most third-party devices in your network and adds them to the topology view of the Security Fabric." It also states that in the interfaces section, you can enable device detection, and this detection is what allows FortiGate to identify devices based on observed traffic.
In the exhibit, the tooltip distinguishes between "1 device requires authorization" and "1 other identified device." That means the unauthorized device is a separate FortiGate/Fabric member issue, while the other identified device is simply a detected third-party device shown in the topology because device detection is working. Therefore, the correct interpretation is that device detection is enabled for that identified device. Option B is incorrect because the exhibit does not say the other identified device requires authorization. Option C is not supported by the study guide, and option D is too specific because no evidence in the exhibit confirms that the detection was enabled specifically on port3.
NEW QUESTION # 101
During layer 2 polling, which two pieces of information are gathered by FortiNAC to identify a device? (Choose two.)
- A. The system name learned
- B. The MAC-to-IP correlation learned
- C. The time it was learned
- D. Where it was learned
Answer: C,D
Explanation:
Layer 2 polling allows FortiNAC to learn where a device appears in the network, such as the switch and port, and when that information was learned. This helps FortiNAC identify and track device presence and location based on Layer 2 network discovery.
NEW QUESTION # 102
......
NSE6_OTS_AR-7.6 Test Questions Answers: https://www.freepdfdump.top/NSE6_OTS_AR-7.6-valid-torrent.html
- NSE6_OTS_AR-7.6 Pass4sure Exam Prep ???? Question NSE6_OTS_AR-7.6 Explanations ???? NSE6_OTS_AR-7.6 Reliable Exam Questions ☝ Search for 「 NSE6_OTS_AR-7.6 」 and download it for free immediately on { www.prep4sures.top } ????Latest NSE6_OTS_AR-7.6 Exam Dumps
- Exam NSE6_OTS_AR-7.6 Forum ???? Exam NSE6_OTS_AR-7.6 Fees ???? Valid NSE6_OTS_AR-7.6 Test Answers ???? Simply search for ➠ NSE6_OTS_AR-7.6 ???? for free download on ➡ www.pdfvce.com ️⬅️ ????PDF NSE6_OTS_AR-7.6 VCE
- Exam NSE6_OTS_AR-7.6 Fees ???? PDF NSE6_OTS_AR-7.6 VCE ???? NSE6_OTS_AR-7.6 Latest Real Test ???? Search on ⇛ www.exam4labs.com ⇚ for 【 NSE6_OTS_AR-7.6 】 to obtain exam materials for free download ????Exam NSE6_OTS_AR-7.6 Fees
- Pass Guaranteed 2026 Fortinet NSE6_OTS_AR-7.6 –Professional Latest Exam Cost ???? Simply search for ▷ NSE6_OTS_AR-7.6 ◁ for free download on 【 www.pdfvce.com 】 ????Dump NSE6_OTS_AR-7.6 File
- Fortinet NSE 6 - OT Security 7.6 Architect Trustworthy exam Practice - NSE6_OTS_AR-7.6 exam training pdf - Fortinet NSE 6 - OT Security 7.6 Architect updated study material ???? Go to website ⮆ www.prepawayexam.com ⮄ open and search for ▷ NSE6_OTS_AR-7.6 ◁ to download for free ????NSE6_OTS_AR-7.6 Latest Test Experience
- Exam NSE6_OTS_AR-7.6 Fees ???? Question NSE6_OTS_AR-7.6 Explanations ???? Dumps NSE6_OTS_AR-7.6 Free Download ???? Search for ☀ NSE6_OTS_AR-7.6 ️☀️ and download it for free immediately on ▷ www.pdfvce.com ◁ ☘NSE6_OTS_AR-7.6 Latest Real Test
- NSE6_OTS_AR-7.6 Reliable Exam Questions ???? Exam NSE6_OTS_AR-7.6 Actual Tests ???? Dump NSE6_OTS_AR-7.6 File ???? ▛ www.examcollectionpass.com ▟ is best website to obtain 《 NSE6_OTS_AR-7.6 》 for free download ????Question NSE6_OTS_AR-7.6 Explanations
- Valid NSE6_OTS_AR-7.6 Study Plan ???? NSE6_OTS_AR-7.6 Latest Test Experience ???? Exam NSE6_OTS_AR-7.6 Forum ⚔ Go to website ▷ www.pdfvce.com ◁ open and search for ➥ NSE6_OTS_AR-7.6 ???? to download for free ????PDF NSE6_OTS_AR-7.6 VCE
- Exam NSE6_OTS_AR-7.6 Collection ???? Valid NSE6_OTS_AR-7.6 Study Plan ???? NSE6_OTS_AR-7.6 Test Result ???? Easily obtain ⮆ NSE6_OTS_AR-7.6 ⮄ for free download through ( www.prepawayexam.com ) ????New NSE6_OTS_AR-7.6 Test Format
- Here's a Quick and Proven Way to Pass NSE6_OTS_AR-7.6 Certification exam ???? Open [ www.pdfvce.com ] enter [ NSE6_OTS_AR-7.6 ] and obtain a free download ????Valid NSE6_OTS_AR-7.6 Study Plan
- Latest NSE6_OTS_AR-7.6 Exam Cost Exam 100% Pass | NSE6_OTS_AR-7.6 Test Questions Answers ???? Search for ➡ NSE6_OTS_AR-7.6 ️⬅️ and download exam materials for free through ➤ www.pdfdumps.com ⮘ ✌Reliable NSE6_OTS_AR-7.6 Exam Online
- www.4shared.com, www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, www.stes.tyc.edu.tw, Disposable vapes
What's more, part of that FreePdfDump NSE6_OTS_AR-7.6 dumps now are free: https://drive.google.com/open?id=1afm8ZcfXAoSYY6kuUc4R0bkR_VRri4AK