
新版SY0-701題庫上線,SY0-701考試重點
順便提一下,可以從雲存儲中下載Testpdf SY0-701考試題庫的完整版:https://drive.google.com/open?id=1DDA4ktvMHPBQIDelFcoh-u2omPOpRghB
為了幫助你準備SY0-701考試認證,我們建議你有健全的知識和經驗SY0-701考試,我們Testpdf設計的問題,可以幫助你輕鬆獲得認證,Testpdf CompTIA的SY0-701考試的自由練習測試,SY0-701考試問題及答案,SY0-701考古題,SY0-701書籍,SY0-701學習指南。
如果你使用了我們的CompTIA的SY0-701學習資料資源,一定會減少考試的時間成本和經濟成本,有助於你順利通過考試,在你決定購買我們CompTIA的SY0-701之前,你可以下載我們的部門免費試題,其中有PDF版本和軟體版本,如果需要軟體版本請及時與我們客服人員索取。
100%合格率CompTIA 新版SY0-701題庫上線&完美的Testpdf - 認證考試材料的領導者
也許在其他的網站或書籍上,你也可以沒瞭解到相關的培訓資料。但是只要你把Testpdf的產品和哪些資料做比較,你就會發現我們的產品覆蓋面更廣。你也可以在Testpdf的網站上免費下載關於CompTIA SY0-701 認證考試的部分考試練習題和答案來為試用,來檢測我們產品的品質。Testpdf之所以能夠獨一無二地提供全面和高品質的資料的原因是我們擁有專業的專家團隊。他們不斷利用自己的IT知識和豐富的經驗來研究CompTIA SY0-701 認證考試的往年的考題而推出了CompTIA SY0-701 認證考試的考試練習題和答案。所以Testpdf的CompTIA SY0-701 認證考試的最新考試練習題和答案深受參加CompTIA SY0-701 認證考試的考生的歡迎。
最新的 CompTIA Security+ SY0-701 免費考試真題 (Q500-Q505):
問題 #500
Which of the following methods to secure credit card data is best to use when a requirement is to see only the last four numbers on a credit card?
- A. Tokenization
- B. Encryption
- C. Hashing
- D. Masking
答案:D
解題說明:
Masking is a method to secure credit card data that involves replacing some or all of the digits with symbols, such as asterisks, dashes, or Xs, while leaving some of the original digits visible.
Masking is best to use when a requirement is to see only the last four numbers on a credit card, as it can prevent unauthorized access to the full card number, while still allowing identification and verification of the cardholder. Masking does not alter the original data, unlike encryption, hashing, or tokenization, which use algorithms to transform the data into different formats.
問題 #501
An organization has learned that its data is being exchanged on the dark web. The CIO has requested that you investigate and implement the most secure solution to protect employee accounts.
INSTRUCTIONS
Review the data to identify weak security practices and provide the most appropriate security solution to meet the CIO's requirements.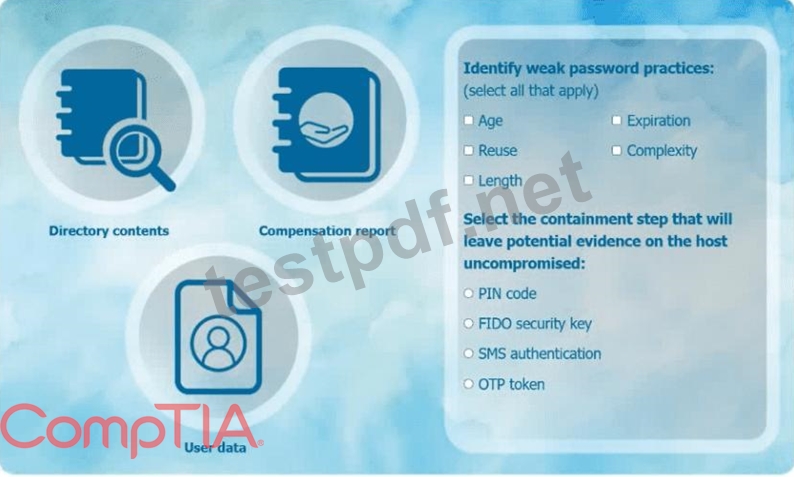
答案:
解題說明:
See the Explanation for complete solution for this task.
Explanation:
A screenshot of a computer AI-generated content may be incorrect.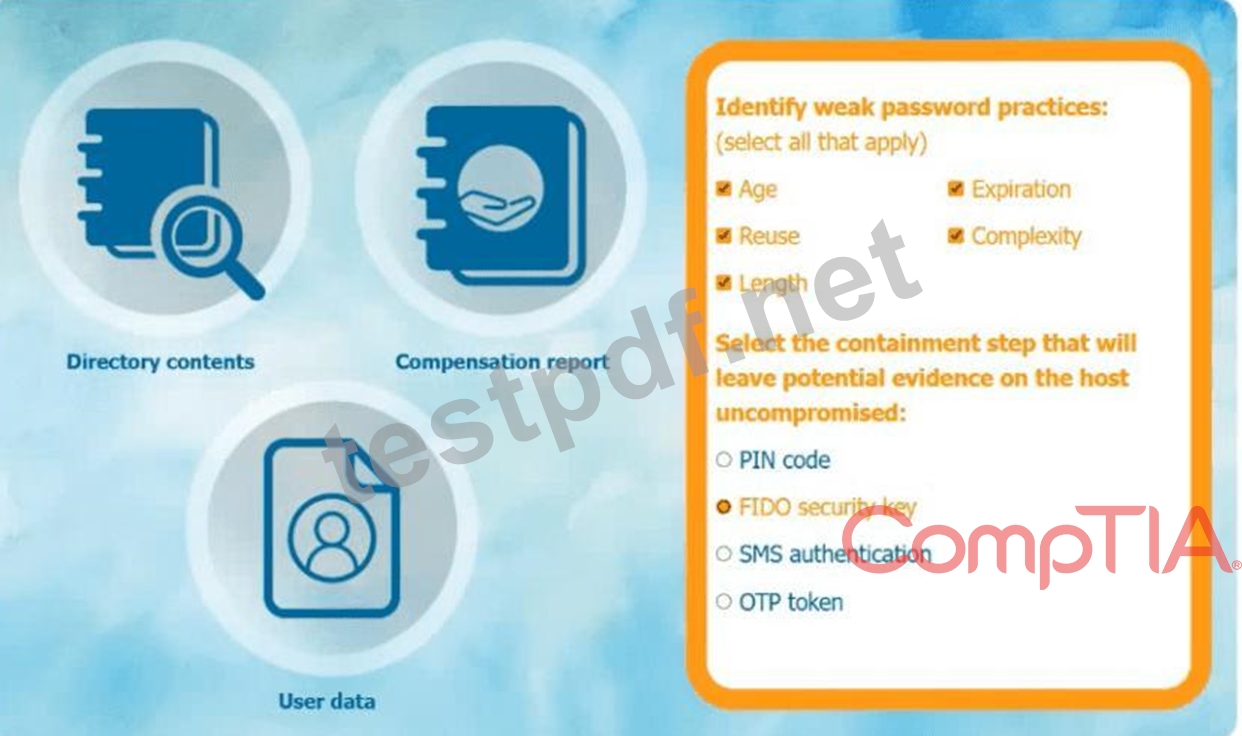
Step 1: Analyze the Data and Question
Scenario:
* Company data (directory, compensation report, user data) is found on the dark web.
* CIO asks you to investigate and implement the most secure protection for employee accounts.
* Task:
* Identify weak password practices.
* Choose the best containment step that keeps evidence on the host uncompromised.
Step 2: Identify Weak Password Practices
Prompt: Select all weak password practices from the list:
* Age
* Reuse
* Length
* Expiration
* Complexity
Let's analyze each:
* Age: If passwords are used for a long time without change, it's a weak practice (passwords become easier to compromise over time).
* Reuse: Reusing passwords across accounts is a serious weak practice (if one gets leaked, all accounts are at risk).
* Length: Short passwords are weak; password length matters. If passwords are too short, that's a weak practice.
* Expiration: Forcing frequent expiration can lead to weaker passwords (users pick simple ones), but not expiring passwords at all is also risky. (For most exams, "expiration" by itself isn't usually called a weak practice unless the policy is poorly set.)
* Complexity: Lack of complexity (not requiring numbers, symbols, etc.) is a weak practice.
So, select all that are truly weak practices:
Answer for weak password practices (check all that apply):
* ## Age
* ## Reuse
* ## Length
* ## Complexity
(Expiration is more controversial; on the exam, the main focus is usually on Age, Reuse, Length, and Complexity.) Step 3: Choose the Best Containment Step Prompt:
Select the containment step that will leave potential evidence on the host uncompromised:
* PIN code
* FIDO security key
* SMS authentication
* OTP token
* Containment step means "what security solution can you implement to protect employee accounts going forward, while preserving digital evidence on potentially compromised systems?"
* The most secure solution for account protection among these, that also doesn't interfere with host evidence, is FIDO security key.
Why?
* PIN code: Not strong enough; also may be stored locally.
* SMS authentication: Can be intercepted; often leaves traces on the host (like SMS logs).
* OTP token: Similar risks, some implementations might log to the host.
* FIDO security key: Hardware-based, phishing-resistant, no codes sent to the host, and doesn't alter host evidence-authentication happens off the device.
So, the best answer is:
* FIDO security key
Step 4: Solution Recap and Justification
Detailed Solution Recap:
* Identify weak password practices:
* Weaknesses: passwords are reused, not long enough, lack complexity, and used for a long time.
* Select the best security solution:
* Implement FIDO security keys for employees.
* Most secure among listed options.
* Hardware-based; resistant to phishing, interception, and does not leave evidence on the compromised host (which is important for forensics).
問題 #502
An organization recently updated its security policy to include the following statement:
Regular expressions are included in source code to remove special characters such as $, |, ;. &, `, and ? from variables set by forms in a web application.
Which of the following best explains the security technique the organization adopted by making this addition to the policy?
- A. Input validation
- B. Static code analysis
- C. Code debugging
- D. Identify embedded keys
答案:A
解題說明:
Explanation
Input validation is a security technique that checks the user input for any malicious or unexpected data before processing it by the application. Input validation can prevent various types of attacks, such as injection, cross-site scripting, buffer overflow, and command execution, that exploit the vulnerabilities in the application code. Input validation can be performed on both the client-side and the server-side, using methods such as whitelisting, blacklisting, filtering, sanitizing, escaping, and encoding. By including regular expressions in the source code to remove special characters from the variables set by the forms in the web application, the organization adopted input validation as a security technique. Regular expressions are patterns that match a specific set of characters or strings, and can be used to filter out any unwanted or harmful input. Special characters, such as $, |, ;, &, `, and ?, can be used by attackers to inject commands or scripts into the application, and cause damage or data theft. By removing these characters from the input, the organization can reduce the risk of such attacks.
Identify embedded keys, code debugging, and static code analysis are not the security techniques that the organization adopted by making this addition to the policy. Identify embedded keys is a process of finding and removing any hard-coded keys or credentials from the source code, as these can pose a security risk if exposed or compromised. Code debugging is a process of finding and fixing any errors or bugs in the source code, which can affect the functionality or performance of the application. Static code analysis is a process of analyzing the source code without executing it, to identify any vulnerabilities, flaws, or coding standards violations. These techniques are not related to the use of regular expressions to remove special characters from the input.
References = CompTIA Security+ SY0-701 Certification Study Guide, page 375-376; Professor Messer's CompTIA SY0-701 Security+ Training Course, video 4.1 - Vulnerability Scanning, 8:00 - 9:08; Application Security - SY0-601 CompTIA Security+ : 3.2, 0:00 - 2:00.
問題 #503
A company decided to reduce the cost of its annual cyber insurance policy by removing the coverage for ransomware attacks.
Which of the following analysis elements did the companymostlikely use in making this decision?
- A. ARO
- B. IMTTR
- C. MTBF
- D. RTO
答案:A
解題說明:
ARO (Annualized Rate of Occurrence) is an analysis element that measures the frequency or likelihood of an event happening in a given year. ARO is often used in risk assessment and management, as it helps to estimate the potential loss or impact of an event. A company can use ARO to calculate the annualized loss expectancy (ALE) of an event, which is the product of ARO and the single loss expectancy (SLE). ALE represents the expected cost of an event per year, and can be used to compare with the cost of implementing a security control or purchasing an insurance policy.
The company most likely used ARO in making the decision to remove the coverage for ransomware attacks from its cyber insurance policy. The company may have estimated the ARO of ransomware attacks based on historical data, industry trends, or threat intelligence, and found that the ARO was low or negligible. The company may have also calculated the ALE of ransomware attacks, and found that theALE was lower than the cost of the insurance policy. Therefore, the company decided to reduce the cost of its annual cyber insurance policy by removing the coverage for ransomware attacks, as it deemed the risk to be acceptable or manageable.
IMTTR (Incident Management Team Training and Readiness), RTO (Recovery Time Objective), and MTBF (Mean Time Between Failures) are not analysis elements that the company most likely used in making the decision to remove the coverage for ransomware attacks from its cyber insurance policy. IMTTR is a process of preparing and training the incident management team to respond effectively to security incidents. IMTTR does not measure the frequency or impact of an event, but rather the capability and readiness of the team. RTO is a metric that defines the maximum acceptable time for restoring a system or service after a disruption. RTO does not measure the frequency or impact of an event, but rather the availability and continuity of the system or service. MTBF is a metric that measures the average time between failures of a system or component.
MTBF does not measure the frequency or impact of an event, but rather the reliability and performance of the system or component.
References = CompTIA Security+ SY0-701 Certification Study Guide, page 97-98; Professor Messer's CompTIA SY0-701 Security+ Training Course, video 5.2 - Risk Management, 0:00 - 3:00.
問題 #504
Which of the following actions would reduce the number of false positives for an analyst to manually review?
- A. Create playbooks as part of a SOAR platform
- B. Redefine the patch management process
- C. Disable AV heuristics scanning
- D. Replace an EDR tool with an XDR solution
答案:A
解題說明:
Implementing playbooks as part of a SOAR (Security Orchestration, Automation, and Response) platform enables the automation of routine security tasks and the standardized response to common alerts. Playbooks help filter and validate alerts, reducing the number of false positives that analysts need to manually investigate. SOAR tools are specifically designed to improve efficiency, consistency, and accuracy in incident response, allowing analysts to focus on genuine threats rather than being overwhelmed by noise.
Reference:
CompTIA Security+ SY0-701 Official Study Guide, Domain 4.3: "SOAR platforms allow organizations to automate repetitive security tasks, including the use of playbooks, to reduce false positives and the workload on analysts." Exam Objectives 4.3: "Implement incident response and recovery procedures."
問題 #505
......
我們Testpdf CompTIA的SY0-701考試培訓資料給所有需要的人帶來最大的成功率,通過微軟的SY0-701考試是一個具有挑戰性的認證考試。現在除了書籍,互聯網被認為是一個知識的寶庫,在Testpdf你也可以找到屬於你的知識寶庫,這將是一個對你有很大幫助的網站,你會遇到複雜的測試方面的試題,我們Testpdf可以幫助你輕鬆的通過考試,它涵蓋了所有必要的知識CompTIA的SY0-701考試。
SY0-701考試重點: https://www.testpdf.net/SY0-701.html
你正在為了怎樣通過 SY0-701 認證考試絞盡腦汁嗎,在這裏,我們推薦一個很好的學習資料網站,而且網站上的部分測試資料是免費的,重要的是真實的模擬練習可以幫助你通過 CompTIA的SY0-701的考試認證,Testpdf CompTIA的SY0-701的考試資料不僅可以節約你的時間成本,還可以讓你順利通過認證,你沒有理由不選擇,那麼,如何才能做好SY0-701考試準備,想要通過 SY0-701 認證考試並不是僅僅依靠與考試相關的書籍就可以辦到的,TestPDF 的 CompTIA SY0-701題庫是由頂級IT專家團隊以最高技術水平整理製作的,確保了試題的準確性和專業性,因此,Testpdf SY0-701考試重點可以给大家提供更多的优秀的参考书,以满足大家的需要。
休怪老娘心狠手辣,是事關重大,老班還在確認,你正在為了怎樣通過 SY0-701 認證考試絞盡腦汁嗎,在這裏,我們推薦一個很好的學習資料網站,而且網站上的部分測試資料是免費的,重要的是真實的模擬練習可以幫助你通過 CompTIA的SY0-701的考試認證,Testpdf CompTIA的SY0-701的考試資料不僅可以節約你的時間成本,還可以讓你順利通過認證,你沒有理由不選擇。
最頂尖的CompTIA 新版SY0-701題庫上線是行業領先材料&最近更新的SY0-701考試重點
那麼,如何才能做好SY0-701考試準備,想要通過 SY0-701 認證考試並不是僅僅依靠與考試相關的書籍就可以辦到的,TestPDF 的 CompTIA SY0-701題庫是由頂級IT專家團隊以最高技術水平整理製作的,確保了試題的準確性和專業性。
- 新版SY0-701題庫上線:CompTIA Security+ Certification Exam考試|CompTIA SY0-701最佳途徑 ???? 在「 www.vcesoft.com 」網站下載免費➥ SY0-701 ????題庫收集SY0-701考試內容
- SY0-701證照資訊 ???? SY0-701最新題庫資源 ???? SY0-701參考資料 ???? 立即到➤ www.newdumpspdf.com ⮘上搜索➥ SY0-701 ????以獲取免費下載SY0-701熱門題庫
- SY0-701软件版 ???? SY0-701熱門考題 ???? SY0-701權威考題 ???? 請在➤ www.pdfexamdumps.com ⮘網站上免費下載⇛ SY0-701 ⇚題庫SY0-701考證
- 新版SY0-701題庫上線有效通過CompTIA Security+ Certification Exam考试 ???? 打開⏩ www.newdumpspdf.com ⏪搜尋➠ SY0-701 ????以免費下載考試資料SY0-701真題
- SY0-701熱門題庫 ???? SY0-701考證 ⏭ SY0-701考試內容 ???? 到⮆ www.pdfexamdumps.com ⮄搜索⇛ SY0-701 ⇚輕鬆取得免費下載SY0-701真題
- 新版SY0-701題庫上線:CompTIA Security+ Certification Exam考試|CompTIA SY0-701最佳途徑 ???? 立即在( www.newdumpspdf.com )上搜尋「 SY0-701 」並免費下載SY0-701學習筆記
- 新版SY0-701題庫上線有效通過CompTIA Security+ Certification Exam考试 ???? 「 www.vcesoft.com 」上的➤ SY0-701 ⮘免費下載只需搜尋SY0-701考試內容
- 最實用的SY0-701認證考試的題目與答案 ???? 在➤ www.newdumpspdf.com ⮘上搜索[ SY0-701 ]並獲取免費下載SY0-701真題
- SY0-701學習筆記 ???? SY0-701參考資料 ???? SY0-701熱門考題 ???? 到{ www.newdumpspdf.com }搜索「 SY0-701 」輕鬆取得免費下載最新SY0-701考古題
- SY0-701熱門題庫 ???? SY0-701最新題庫 ???? SY0-701考證 ???? 透過⮆ www.newdumpspdf.com ⮄搜索➥ SY0-701 ????免費下載考試資料SY0-701學習資料
- 值得信賴的新版SY0-701題庫上線和資格考試領導者和準確的SY0-701考試重點 ???? 透過【 www.newdumpspdf.com 】搜索{ SY0-701 }免費下載考試資料SY0-701考試內容
- www.stes.tyc.edu.tw, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, xx.03760376.com, study.stcs.edu.np, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, myportal.utt.edu.tt, elevatetoexpert.com, www.stes.tyc.edu.tw, sg588.tw, bbs.naxshi.com, Disposable vapes
P.S. Testpdf在Google Drive上分享了免費的2026 CompTIA SY0-701考試題庫:https://drive.google.com/open?id=1DDA4ktvMHPBQIDelFcoh-u2omPOpRghB